Pentesting.
Your scope.
Your budget.
Manual testing for complex investigations. Agentic pentesting for repeatable web and API checks. Choose the scope and budget with us.
The application.
And everything around it.
Start with what you need tested. We’ll work through the scope and the testing approach together.
Web applications & APIs
Authentication, access control, tenant isolation, APIs and business logic.
AI-enabled applications
Test the permissions, tools and data access around your AI features.
Infrastructure
External exposure and internal attack paths across your network, systems and services.
Cloud security
Cloud configuration, identity permissions and exposed services, assessed in the context of your environment.
Need something else? See all services ↗
Your AI features.
Let’s test the boundaries.
Security testing for AI applications, plus agentic pentesting for web and API assessments.
What can your
AI actually access?
Prompt injection, retrieval permissions, cross-user data exposure and agent tool actions. Including MCP integrations where in scope.
AI application testing ↗Agentic pentesting.
Automated checks.
AI-directed checks, automated request handling and manual validation. Read how the approach affects coverage, turnaround and cost.
Explore agentic pentesting ↗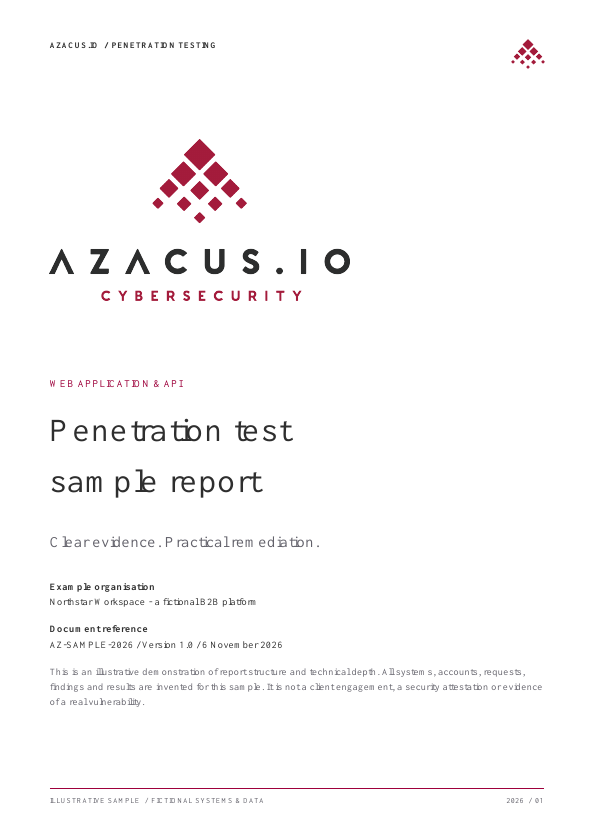 SAMPLE DELIVERABLE / 2026
The exploit.
The impact.
The fix.
Each finding includes reproduction steps, demonstrated impact and remediation guidance.
8-page PDF · Fictional systems · No email required
Scope, test, report.
Then verify the fixes.
Scoping, testing, reporting and verification, with direct access to the tester.
Agree the scope.
Applications, roles, access and deadlines. We agree the scope, fee and deliverables before testing.
Run the assessment.
Test the controls and the workflows around them. Significant findings are communicated during the engagement.
Document the findings.
Reproducible findings, demonstrated impact and practical recommendations for your developers.
Verify remediation.
Discuss remediation and validate agreed fixes. Retesting terms are set out in the proposal.
What does a pentest cost?
It depends on the application, its roles and integrations, and the depth required. Send us the scope and we’ll put together a fixed-fee proposal.
Will the report work for our customer’s security review?
We provide an executive summary and technical evidence you can share. Tell us about any mandatory accreditation, reporting format or customer requirement before booking so we can confirm the engagement fits.
Is retesting included?
Retesting scope, timing and fees are stated in your proposal. We also discuss the findings with your team so the remediation work is clear.
AI application testing or agentic pentesting?
AI application testing examines your AI features, including data access, prompt injection and tool permissions. Agentic pentesting uses AI agents to carry out parts of a security assessment, with manual review of findings.
What do you
need tested?
Tell us about your application, infrastructure or upcoming deadline. We’ll work through the scope with you and put together a proposal.
ping [at] azacus.io ↗Prefer a call? 0131 287 7869
Please don’t include credentials or sensitive testing data here.